

The Manufacturer’s Guide to the Cyber Resilience Act
A free, step-by-step guide through the CRA for manufacturers of connected products, from scope and product categories to vulnerability reporting, conformity assessment, and CE marking.
What’s inside the guide?
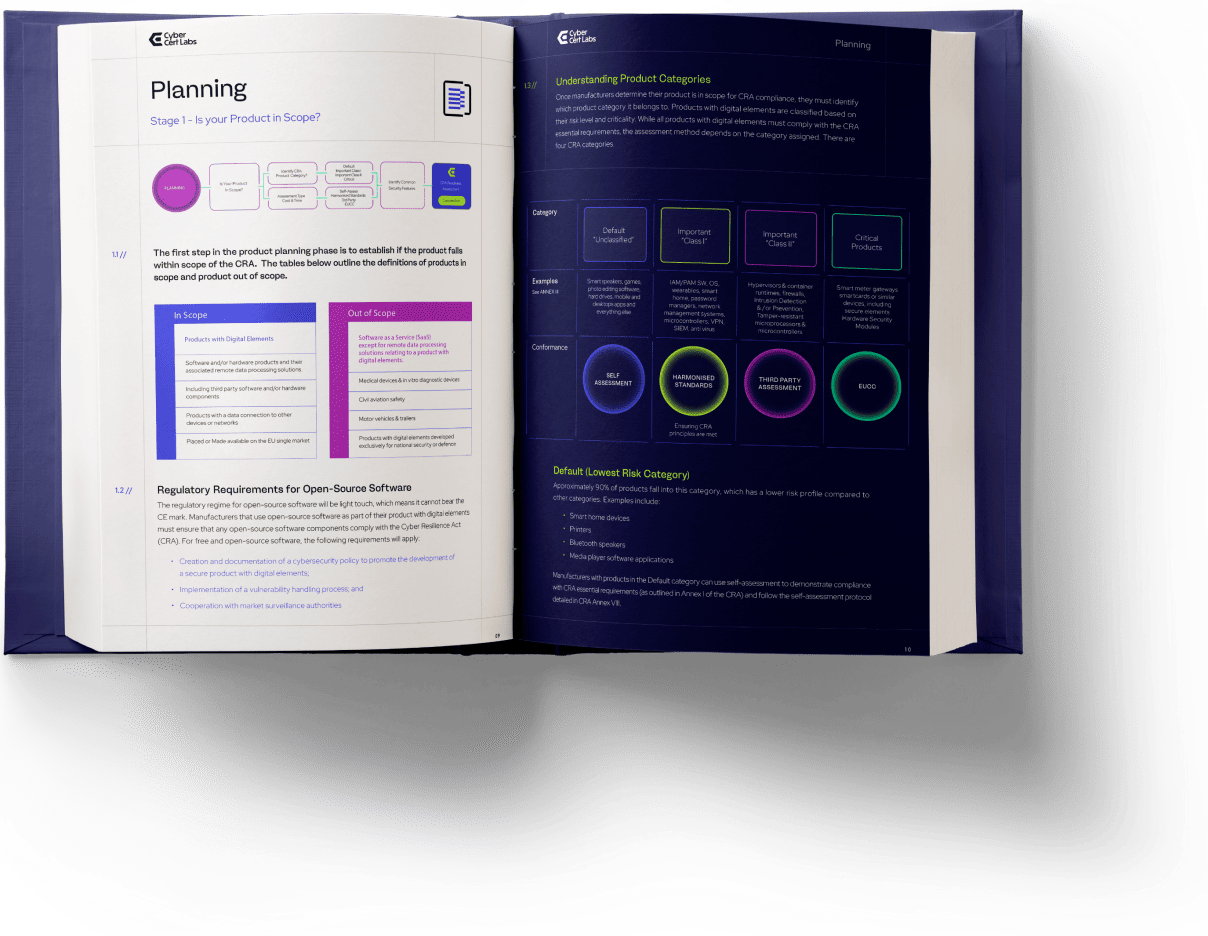
The guide maps the CRA’s requirements to each stage of your product development lifecycle.
-
Planning
How to determine whether your products are in scope, including remote data processing solutions and third-party components. The four product categories and what each means for your conformity assessment route.
-
Design
Security by design and default in practical terms, covering risk assessment, threat modelling, target of evaluation, and protection profiles.
-
Development
The security testing your products will need before release, from secure code analysis and vulnerability testing through to penetration testing. How substantial modifications trigger a fresh assessment.
-
Release
Documentation obligations, support period requirements, SBOM, and the EU declaration of conformity. Everything that must be in place before you can affix the CE mark.
-
Maintenance
Vulnerability reporting obligations in full, including the 24-hour, 72-hour, and 14-day reporting windows. Coordinated vulnerability disclosure and your obligation to inform impacted users.
The guide also covers the penalties for non-compliance, which reach up to €15 million or 2.5% of global turnover, and the specific provisions that apply to SMEs.
Who is this guide for?

Two deadlines manufacturers must be aware of
-

11 September 2026: Vulnerability reporting is live
This deadline has passed. If an actively exploited vulnerability is discovered in your product today, you are legally required to report it to your national CSIRT and ENISA within 24 hours.
-
11 December 2027: Full CRA compliance
Every product with digital elements placed on the EU market must meet the CRA's essential requirements and carry the CE mark. Products that do not comply cannot be sold in the EU, and non-compliance penalties reach up to €15 million or 2.5% of global turnover.