

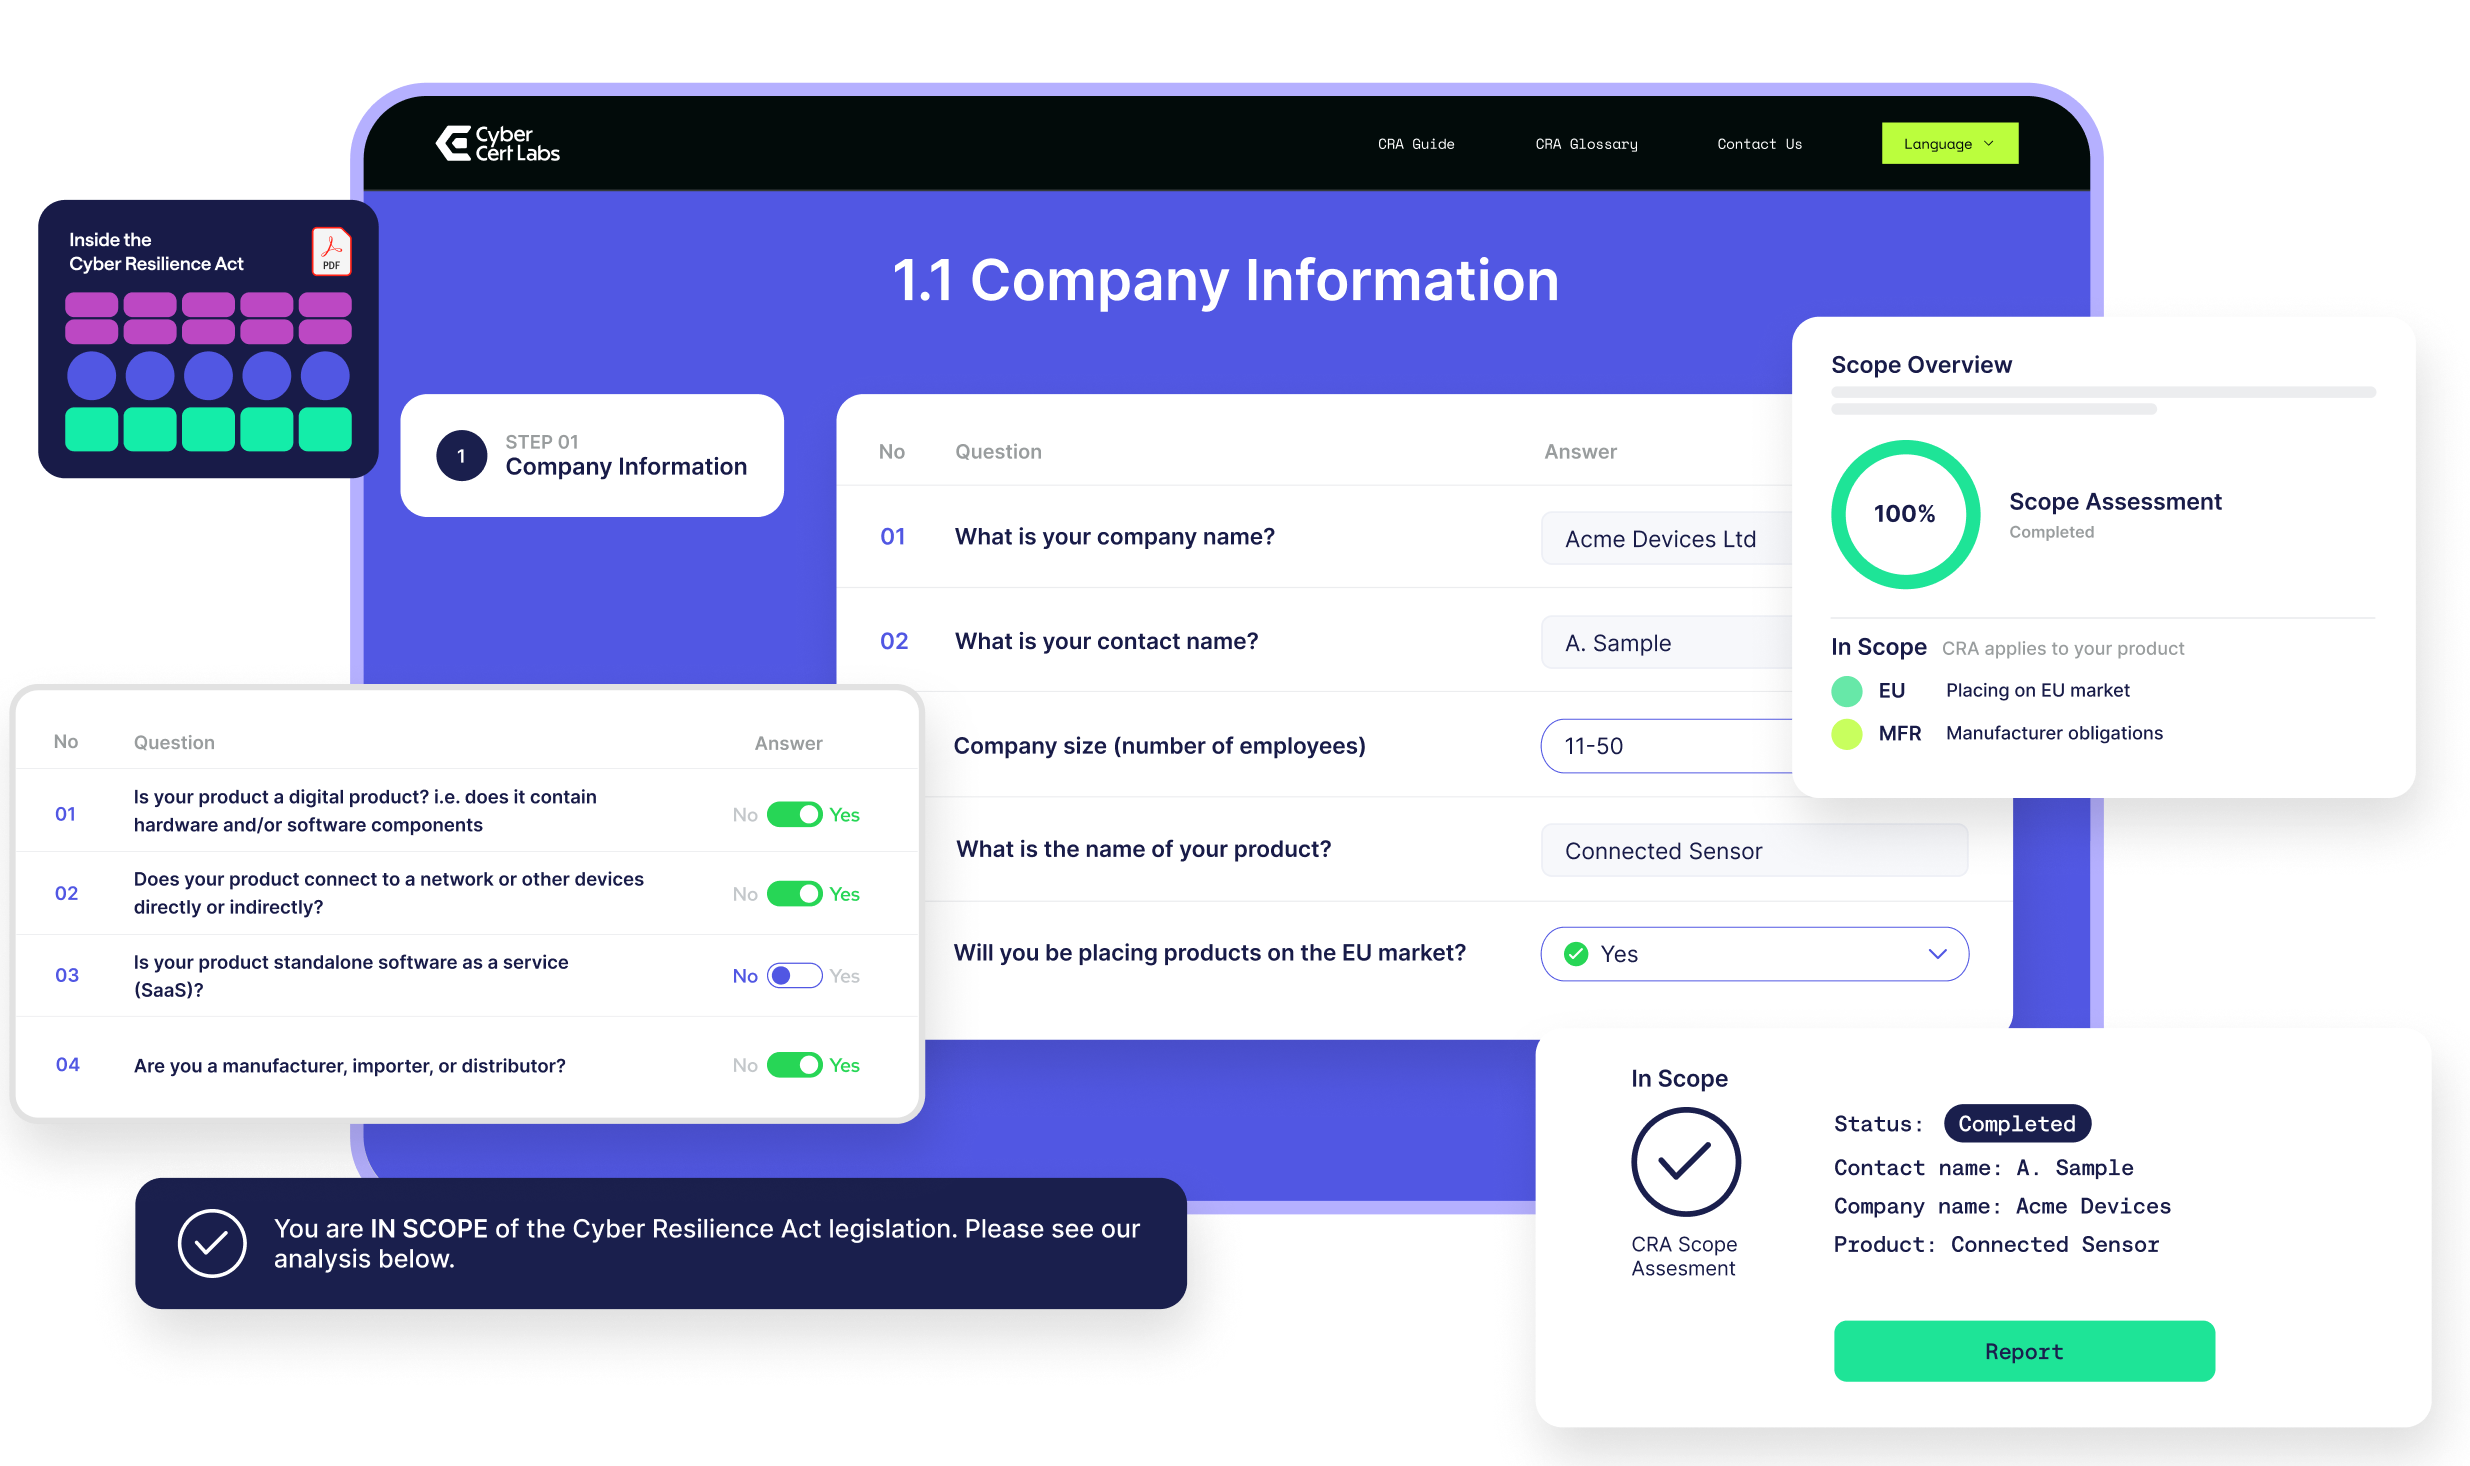
Does the Cyber Resilience Act apply to your product?
The CRA applies to more products than most manufacturers realise. If your product has software, firmware, or a network connection and is sold into the EU, you may already have obligations.
Our free Scope Assessment takes five minutes and tells you where you stand.
Find out if the CRA applies to you
Your scope score, explained
-

The rationale behind it
The specific reasons your product is or is not in scope, mapped against the CRA's definition of products with digital elements.
-

What to do next
If you are in scope, the report points you to the free CRA Readiness Assessment, where you can see exactly where you stand against the requirements.
Take the Readiness Assessment
Your next step if you are in scope

-
 Take the CRA Readiness Assessment
If you have already completed the Scope Assessment and are ready for the next step:
FAQs
The Cyber Resilience Act is EU legislation that sets mandatory cybersecurity requirements for products with digital elements made available on the EU market. It applies to any product with software, hardware, or firmware that has a data connection to a device or network, and it covers the full product lifecycle from design through to end of life. The legislation requires manufacturers to meet essential security requirements, handle vulnerabilities, and obtain CE marking for cybersecurity before placing products on the market.
Any software or hardware product with a data connection to a device or network, including software and hardware components sold separately, and any associated remote data processing. This covers connected devices, IoT products, embedded systems, and standalone software applications. If your product connects to the internet, a local network, or another device, it is very likely in scope.
Yes. The CRA applies to manufacturers, importers, and distributors who make products available on the EU single market, regardless of where they are based. If your product is sold or distributed in the EU, you need to comply.
The CRA does not apply to Software as a Service (except remote data processing solutions linked to a product with digital elements), medical devices, in vitro diagnostic devices, civil aviation products, motor vehicles, products developed exclusively for national security or defence, and products designed to process classified information. These are covered by other specific regulations.
The first obligation begins on 11 September 2026, when vulnerability and incident reporting requirements come into force. Full CRA compliance, including all essential requirements and CE marking, applies from 11 December 2027.
If the assessment determines your product is out of scope, you will receive a rationale explaining why. This is useful documentation for internal records and for answering questions from customers or supply chain partners who may ask about your CRA status.