
Cyber Cert Labs' CRA Readiness Assessment was exactly what we needed. The simple, well-structured process with helpful hints made technical aspects clear. The comprehensive report pinpointed exactly where we need to focus for compliance, with clear scores and detailed explanations. This practical guidance is invaluable for aligning with the CRA.


How ready are
you for the Cyber Resilience Act?
You know the CRA applies to your products. The next question is where you stand against its requirements, and where the gaps are.
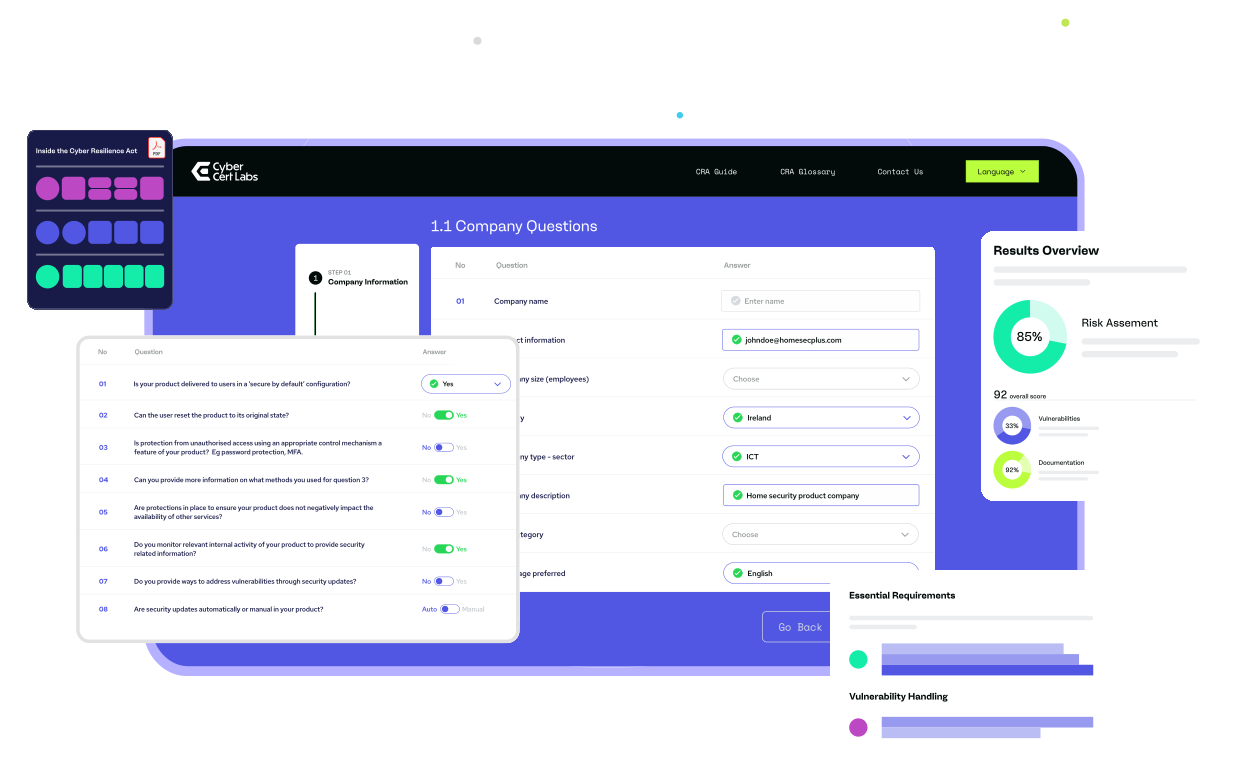
Our free Readiness Assessment takes around 30 minutes and gives you a detailed report scoring your product’s security against the CRA’s essential requirements, with tailored recommendations for what to do next.
Get a clear picture of where you stand today
Your readiness report breakdown
-
A product security scorecard
Your product scored against the CRA essential requirements, with clear ratings across each area so you can see at a glance where you are strong and where you need work.
-
Tailored recommendations
Specific, actionable guidance based on your answers, telling you what to focus on first and why. These are mapped to the CRA requirements, so you know exactly which obligations each recommendation addresses.
-
An SME guide to the Cyber Resilience Act
Walking you through the regulation, the product categories, the conformity assessment routes, and the timeline.
-
A prioritised next-steps plan
A clear view of what to do after the assessment, whether that means training your team, setting up vulnerability handling, or working through the full CRA compliance journey.
Readiness Assessment
Key CRA deadlines are approaching
11 September deadline: Applies to all products already on the market.
11 December deadline: Applies only to products placed on the market after this date, including new products and substantially modified versions of existing products.

-

11 September 2026
Vulnerability reporting obligations are already live. Manufacturers must report actively exploited vulnerabilities to their national CSIRT and to ENISA within 24 hours, with a full report within 14 days.
-
11 December 2027
Full CRA compliance. All in-scope products must meet the CRA's essential requirements, including conformity assessment and CE marking for cybersecurity.
Why most manufacturers find this difficult
-
Uncertainty about what to do
The CRA introduces obligations that most product teams have never had to think about, from vulnerability disclosure processes to software bills of materials. Knowing where to start is the first hurdle.
-
The cost of getting it wrong
Beyond the fines, a product found non-compliant can be recalled or withdrawn from the EU market. For manufacturers whose revenue depends on European customers, that is an existential risk.
-
Limited cybersecurity expertise in-house
Most SMEs and mid-cap manufacturers do not have dedicated cybersecurity or compliance specialists. The people who understand the products are engineers, not security consultants, and the CRA requires them to take on responsibilities they have not been trained for.
-
A compliance process that covers the full product lifecycle
The CRA is not a one-off certification. It requires ongoing vulnerability monitoring, security updates, and reporting for the entire support period of the product, which must be a minimum of five years.
30 minutes from start to action plan
-

Complete the guided questionnaire
The assessment walks you through a structured set of questions about your product, your security practices, and your current processes. It is designed to be completed by a product owner, CTO, or engineering lead without specialist cybersecurity knowledge. Helpful hints throughout explain what each question is asking and why it matters.
-

Plan what to do next
Use the recommendations in your report to build a realistic plan. From your readiness report, you can move into Attestra AI to work through the full CRA compliance journey, or into Attestra Academy to train your team to own compliance internally.
-

Receive your readiness report
A detailed breakdown of your strengths and gaps, scored against the CRA essential requirements. You will see exactly which areas need attention and what the CRA requires in each.
-

Read the SME guide
Gain a deeper understanding of the CRA's requirements, the product categories, the conformity assessment routes, and what the regulation means in practice for your products.
From your report to full CRA compliance
Trusted by:
-
Explore Attestra AI
Attestra AI
Guides manufacturers through the full CRA compliance journey, from vulnerability reporting through to conformity assessment and CE marking. It covers the five stages of the CRA product lifecycle and is built specifically for the regulation, with AI-powered guidance at each step.
-
Explore Attestra Academy
Attestra Academy
Trains your product engineers, product owners, and QA teams to own CRA compliance internally across the full CRA product lifecycle.
Haven’t taken the Scope Assessment yet?
Start with scope if you are unsure
If you do not yet know whether the CRA applies to your product, start with the free CRA Scope Assessment. It takes five minutes and gives you a clear in-scope or out-of-scope determination with a rationale report.
Take the free Scope AssessmentFAQs
The Cyber Resilience Act is EU legislation that sets mandatory cybersecurity requirements for products with digital elements made available on the EU market. It requires manufacturers to meet essential security requirements across the product lifecycle, handle vulnerabilities through a formal process, report incidents to national authorities, and obtain CE marking for cybersecurity.
The assessment is designed for product owners, CTOs, engineering managers, and compliance leads at companies that manufacture or distribute products with digital elements on the EU market. You do not need specialist cybersecurity knowledge to complete it. The guided format with helpful hints makes the process accessible for technical teams who understand their products but may be new to the CRA’s specific requirements.
Around 30 minutes. It is a guided questionnaire, so the time depends on how much detail you have to hand about your product’s current security practices. Having your product documentation and a basic understanding of your vulnerability handling process (or lack of one) will help you get the most from it.
The assessment evaluates your product against the CRA’s essential requirements, covering areas including vulnerability handling, security by design, risk assessment, documentation, and incident reporting readiness. Your report scores each area individually so you can see exactly where you are prepared and where you need to focus.
The CRA defines four categories based on risk. Around 90% of products fall into the Default category, which allows self-assessment. Important Class I products can self-assess if they apply harmonised standards or common specifications. Important Class II products require third-party conformity assessment. Critical Class products require assessment under the European Common Criteria certification scheme. Your Readiness Assessment report will help you understand which category your product falls into.
Failure to comply with CRA essential requirements or reporting obligations can result in administrative fines of up to €15 million or 2.5% of global turnover, whichever is higher. Failure to comply with other obligations carries fines of up to €10 million or 2% of global turnover. Supplying misleading information carries fines of up to €5 million or 1% of global turnover. Non-compliant products can be recalled or withdrawn from the EU market.
Yes. Any manufacturer, importer, or distributor who makes products with digital elements available on the EU single market must comply, regardless of where the company is headquartered.